

POST /events. Use it when usage already lands in your warehouse and you would rather not build an event pipeline. Access is granted through service-account impersonation, so no credentials are shared. Usage sources are described together in How Alguna works; the sibling connector is ClickHouse.
Pre-requisites
This guide assumes that you have an existing dataset and table in your Google Cloud project, and the relevant permissions to create a service account in your Google Cloud project.Overview
Permissions
Alguna leverages Service Account Impersonation as a means to allow you to give access to resources in your Google Cloud project without sharing your own credentials. This is done as follows:- Create a service account in your Google Cloud project with the necessary permissions.
- Give Alguna’s service account the necessary permissions to impersonate the service account in your project.
Process
Data is retrieved from your BigQuery dataset in a two stage process:- Alguna starts a BigQuery
EXPORT DATAjob to export and compress data to a Google Cloud Storage bucket for temporary staging. - Alguna fetches the data from the Google Cloud Storage bucket and ingests it as events.
Setup Resources
This guide shows the setup steps in the GCP console, but you can also do this via IaC.Create a Service Account
-
In the Google Cloud Console for your project, navigate to
IAM & Admin>Service Accounts. -
Click on the
Create Service Accountbutton. -
Give your service account a name, ID and description.
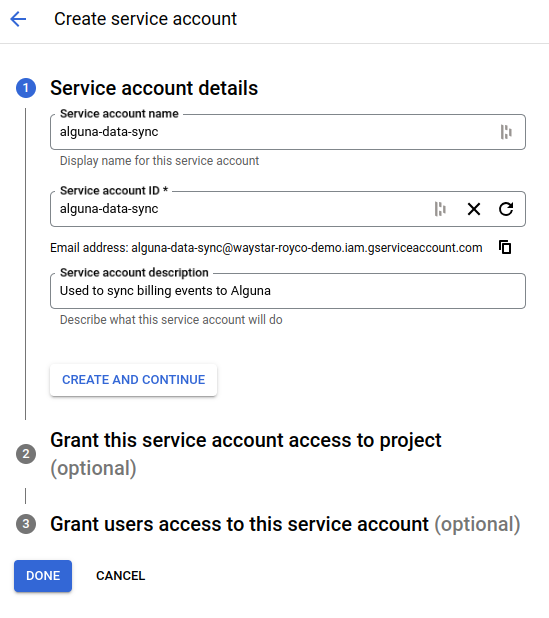
-
Grant the service account the Role
BigQuery Job User.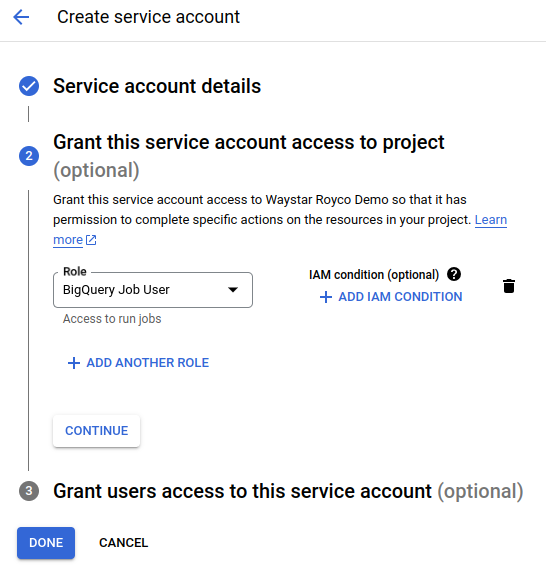
- Make a note of the email address of the service account, as you will need this later. It will be in the format:
Create a Cloud Storage bucket
Fetching data from BigQuery requires a Google Cloud Storage bucket to temporarily compress and store the data before it is ingested into Alguna.-
In the Google Cloud Console for your project, navigate to
Cloud Storage>Buckets. -
Click on the
Createbutton. - Give your bucket a name, and select a single region for the bucket. This must be the same region as your BigQuery dataset.
-
Set the
Storage classtoStandard. -
Check
Enforce public access prevention on this bucketand set theAccess controltoUniform. -
Keep the default settings for
Data Protectionand clickCreate.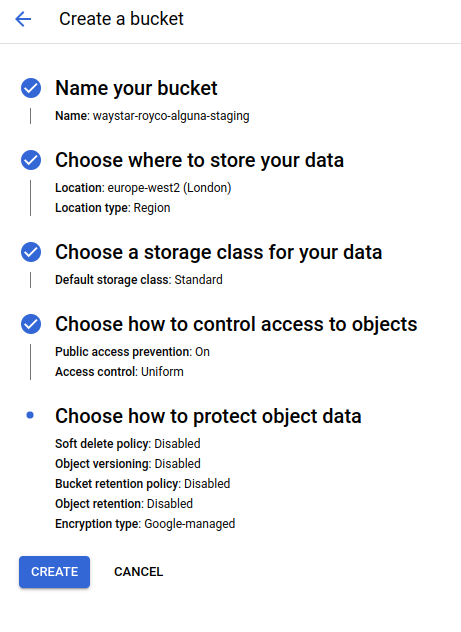
Setup Permissions
Using the email address of the service account you created earlier, grant the following permissions:Project
Grant the service account theBigQuery Job User role on the project, if you didn’t already do this when creating the service account.
This allows the user to submit the EXPORT DATA job to BigQuery.
Cloud Storage
-
On the bucket you created earlier, navigate to the
Permissionstab and clickGrant Access. - Enter the principal email address of the service account you created earlier.
-
Select the role
Storage Object Admin. -
Click
Save.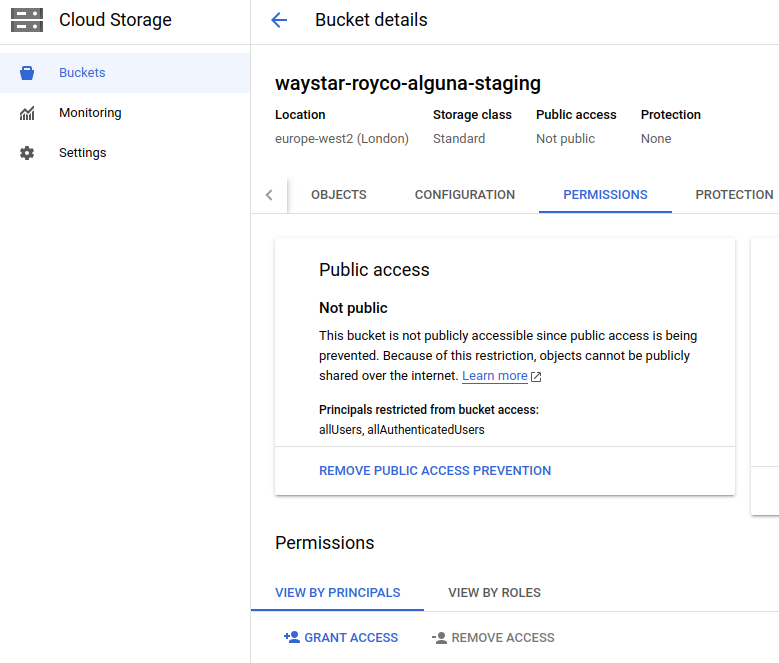
BigQuery
-
In the Google Cloud Console for your project, navigate to
BigQuery. -
Click on the menu next to the table you want to export and select
Share>Manage Permissions. -
Click
Add Principal. - Enter the principal email address of the service account you created earlier.
-
Select the role
BigQuery Data Viewer. -
Click
Save.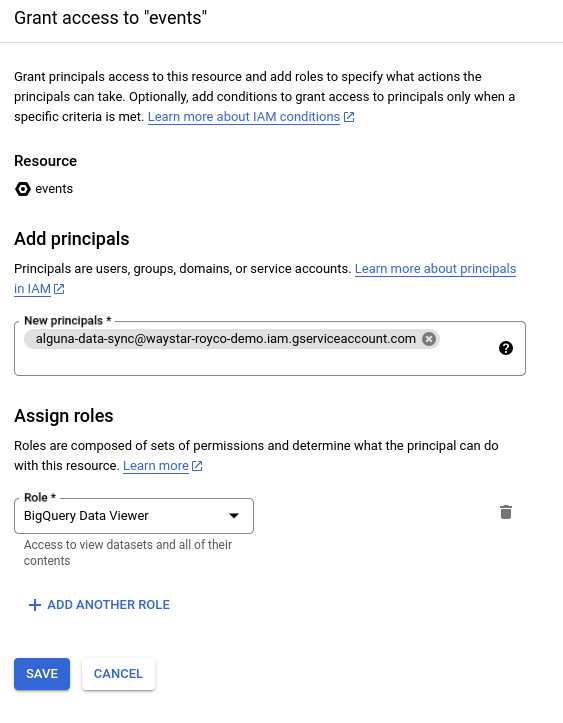
Grant Alguna Access
-
In the Google Cloud Console for your project, navigate to
IAM & Admin>Service Accounts. - Click on the email address of the service account you created earlier.
-
Navigate to the
Permissionstab. -
Select
View By Principals>Grant Access. -
Enter the Alguna service account email address:
-
Select the role
Service Account Token Creator. -
Click
Save.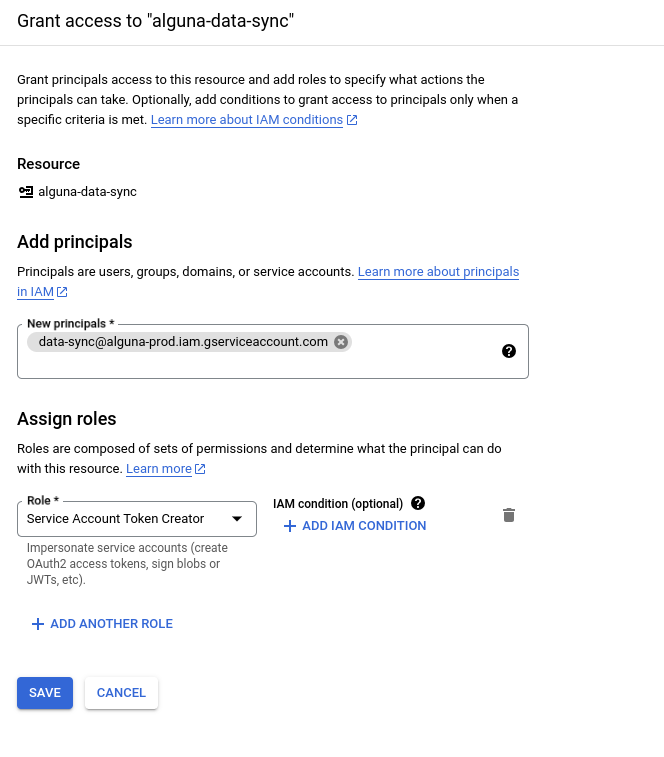
Share Setup Information
Once that’s done, you can share the following information with Alguna:- The email address of the service account you created.
- The name and region of the Google Cloud Storage bucket you created.
- The id of the BigQuery dataset and table you want to export in the format
<projectID>.<datasetID>.<tableID>. - Your table schema, including which columns hold the customer account (an Alguna ID or alias), the event name, the timestamp, and a unique event ID for deduplication — the same fields an event sent to the API carries.
Related
- Send usage events — the event shape rows are mapped onto, and the API and CSV alternatives
- Create metrics — aggregating the ingested events
- ClickHouse — the same integration for ClickHouse tables